
Review of a PG Settlement Management Service Agreement: Payment Suspension and Cybersecurity Liability
Case Overview
- Client Information
- Corporate / Business Entity
- Case Details
-
The client was preparing to adopt an external solution designed to consolidate settlement data generated through payment gateway providers and support the allocation and transfer of settlement funds.
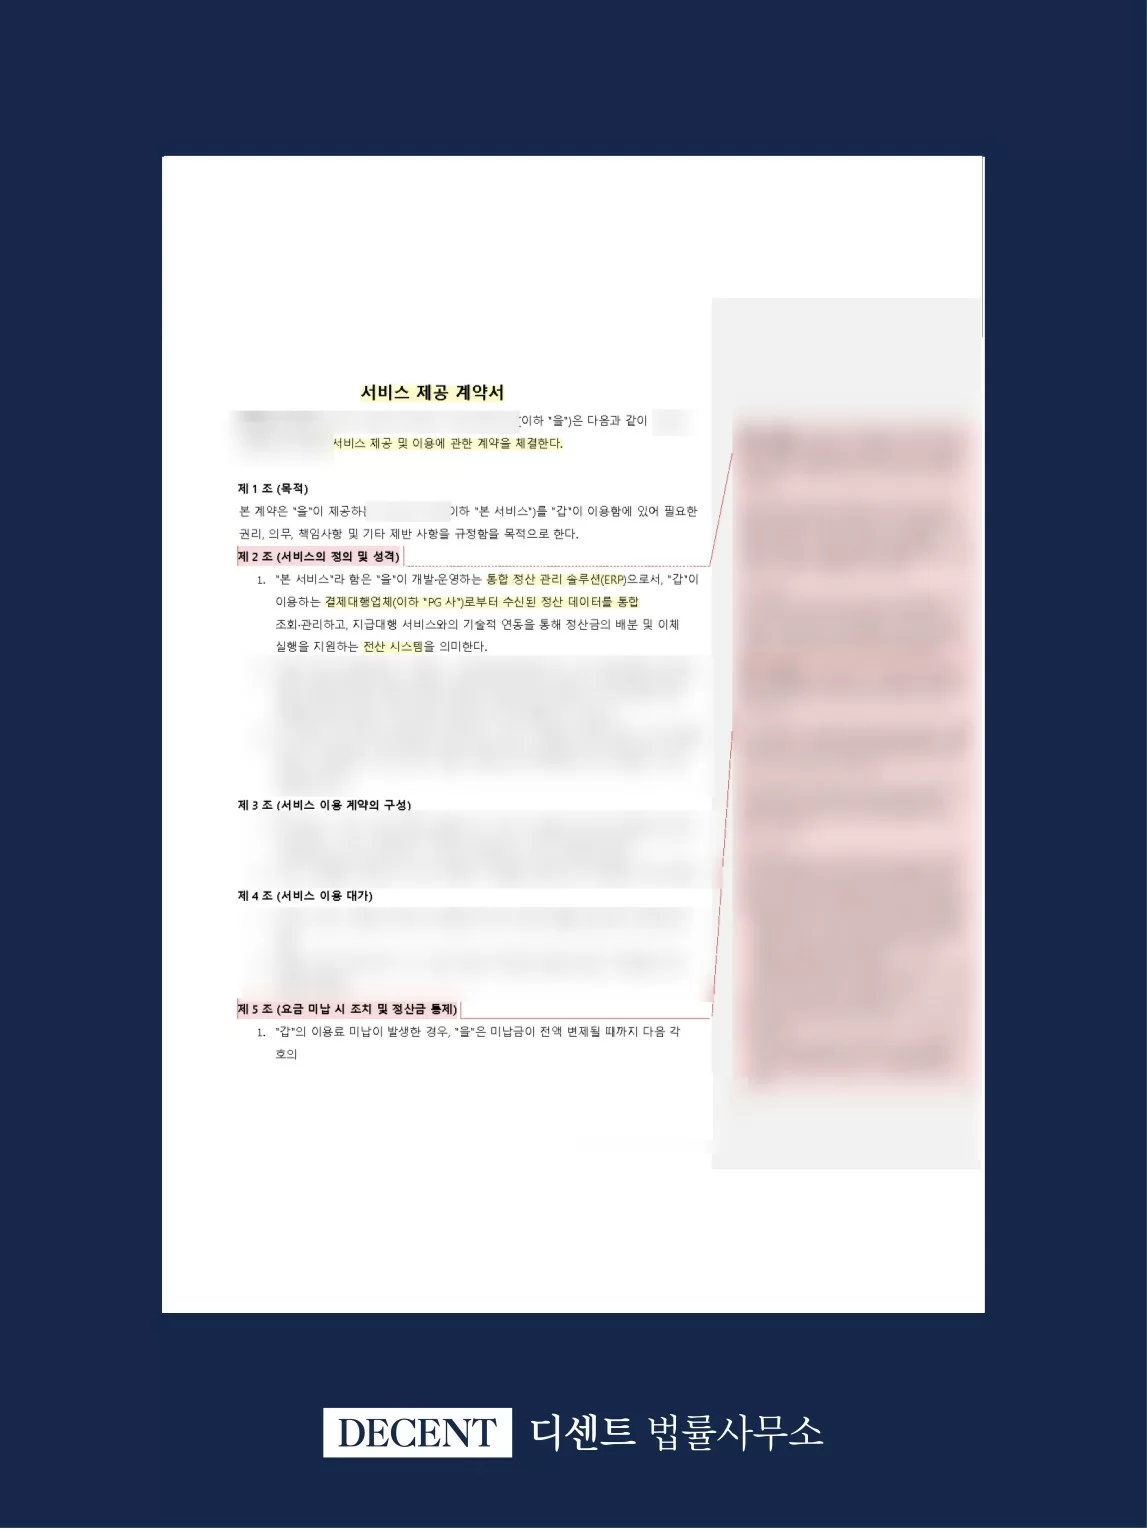
The proposed service agreement included provisions concerning restrictions on settlement payments in the event of unpaid service fees, liability for cybersecurity incidents, limitations on damages, service suspension, and the handling of data following termination.
Before signing the agreement, the client asked Decent Law Firm to assess whether the service provider had been granted overly broad authority and whether liability for potential incidents could be unfairly shifted to the client.
Decent's Strategy
We first examined the contractual structure under which the service provider limited its responsibility for the flow of settlement funds while retaining the authority to restrict transfers due to unpaid fees or concerns about potential incidents.
We recommended clarifying the scope and requirements of any payment restriction so that it could not be imposed beyond the amount of unpaid fees or the level of actual risk involved. We also advised that, as a general rule, the client should receive advance notice and an opportunity to provide an explanation or take corrective action.
With respect to cybersecurity incidents, the agreement imposed specific obligations on the client, including password management and two-factor authentication, while describing the service provider’s own security obligations only in broad terms.
We therefore recommended specifying the security measures to be implemented by the service provider, including data encryption, access control, retention of access logs, monitoring for suspicious activity, incident investigation, and recovery support.
For the limitation of liability provisions, we advised maintaining a reasonable liability cap for ordinary negligence while excluding losses caused by the service provider’s willful misconduct or gross negligence from that limitation.
We also proposed objective criteria to prevent the suspension of services or settlement payments based solely on an unsubstantiated suspicion of unlawful use.
In addition, we recommended requiring the service provider to return data in a commonly usable format following termination and prohibiting the use of retained data for any purpose other than compliance with applicable legal retention requirements.
Results & Significance
1. Clarification of Settlement Payment Restrictions
We recommended limiting any restriction on settlement payments to the amount of unpaid fees and the extent reasonably necessary to preserve the service provider’s claim, so that unpaid service fees would not result in the suspension of the client’s entire settlement operation.
Except in urgent circumstances, the service provider would also be required to provide advance notice and allow the client an opportunity to explain the situation or take corrective action.
This reduced the risk of the service provider exercising its contractual authority in an excessive or disproportionate manner.
2. Balanced Allocation of Cybersecurity Liability
We clarified not only the client’s account management obligations but also the security measures and incident response duties to be performed by the service provider.
Liability for a cybersecurity incident would not automatically be attributed to the client. Instead, responsibility would be assessed based on the actual cause of the incident and the respective areas of management and control of both parties.
3. Revision of Liability Limitations and Payment Suspension Requirements
We recommended that the general limitation of liability should not apply to losses caused by the service provider’s willful misconduct or gross negligence.
We also clarified the objective grounds, notice procedures, and conditions for lifting a payment suspension so that settlement payments could not be suspended solely on the basis of a general or unsupported suspicion.
4. Establishment of Post-Termination Data Handling Standards
We recommended specifying the timing, format, and procedures for the return and deletion of data following termination of the agreement.
Where certain records were required to be retained under applicable law, access would be restricted and the data could not be used for any purpose unrelated to the legally required retention.
Legal Consultation
All consultations are conducted after a case review by the attorney in charge.
Providing the key details of your case in advance will help you receive more specific advice.